
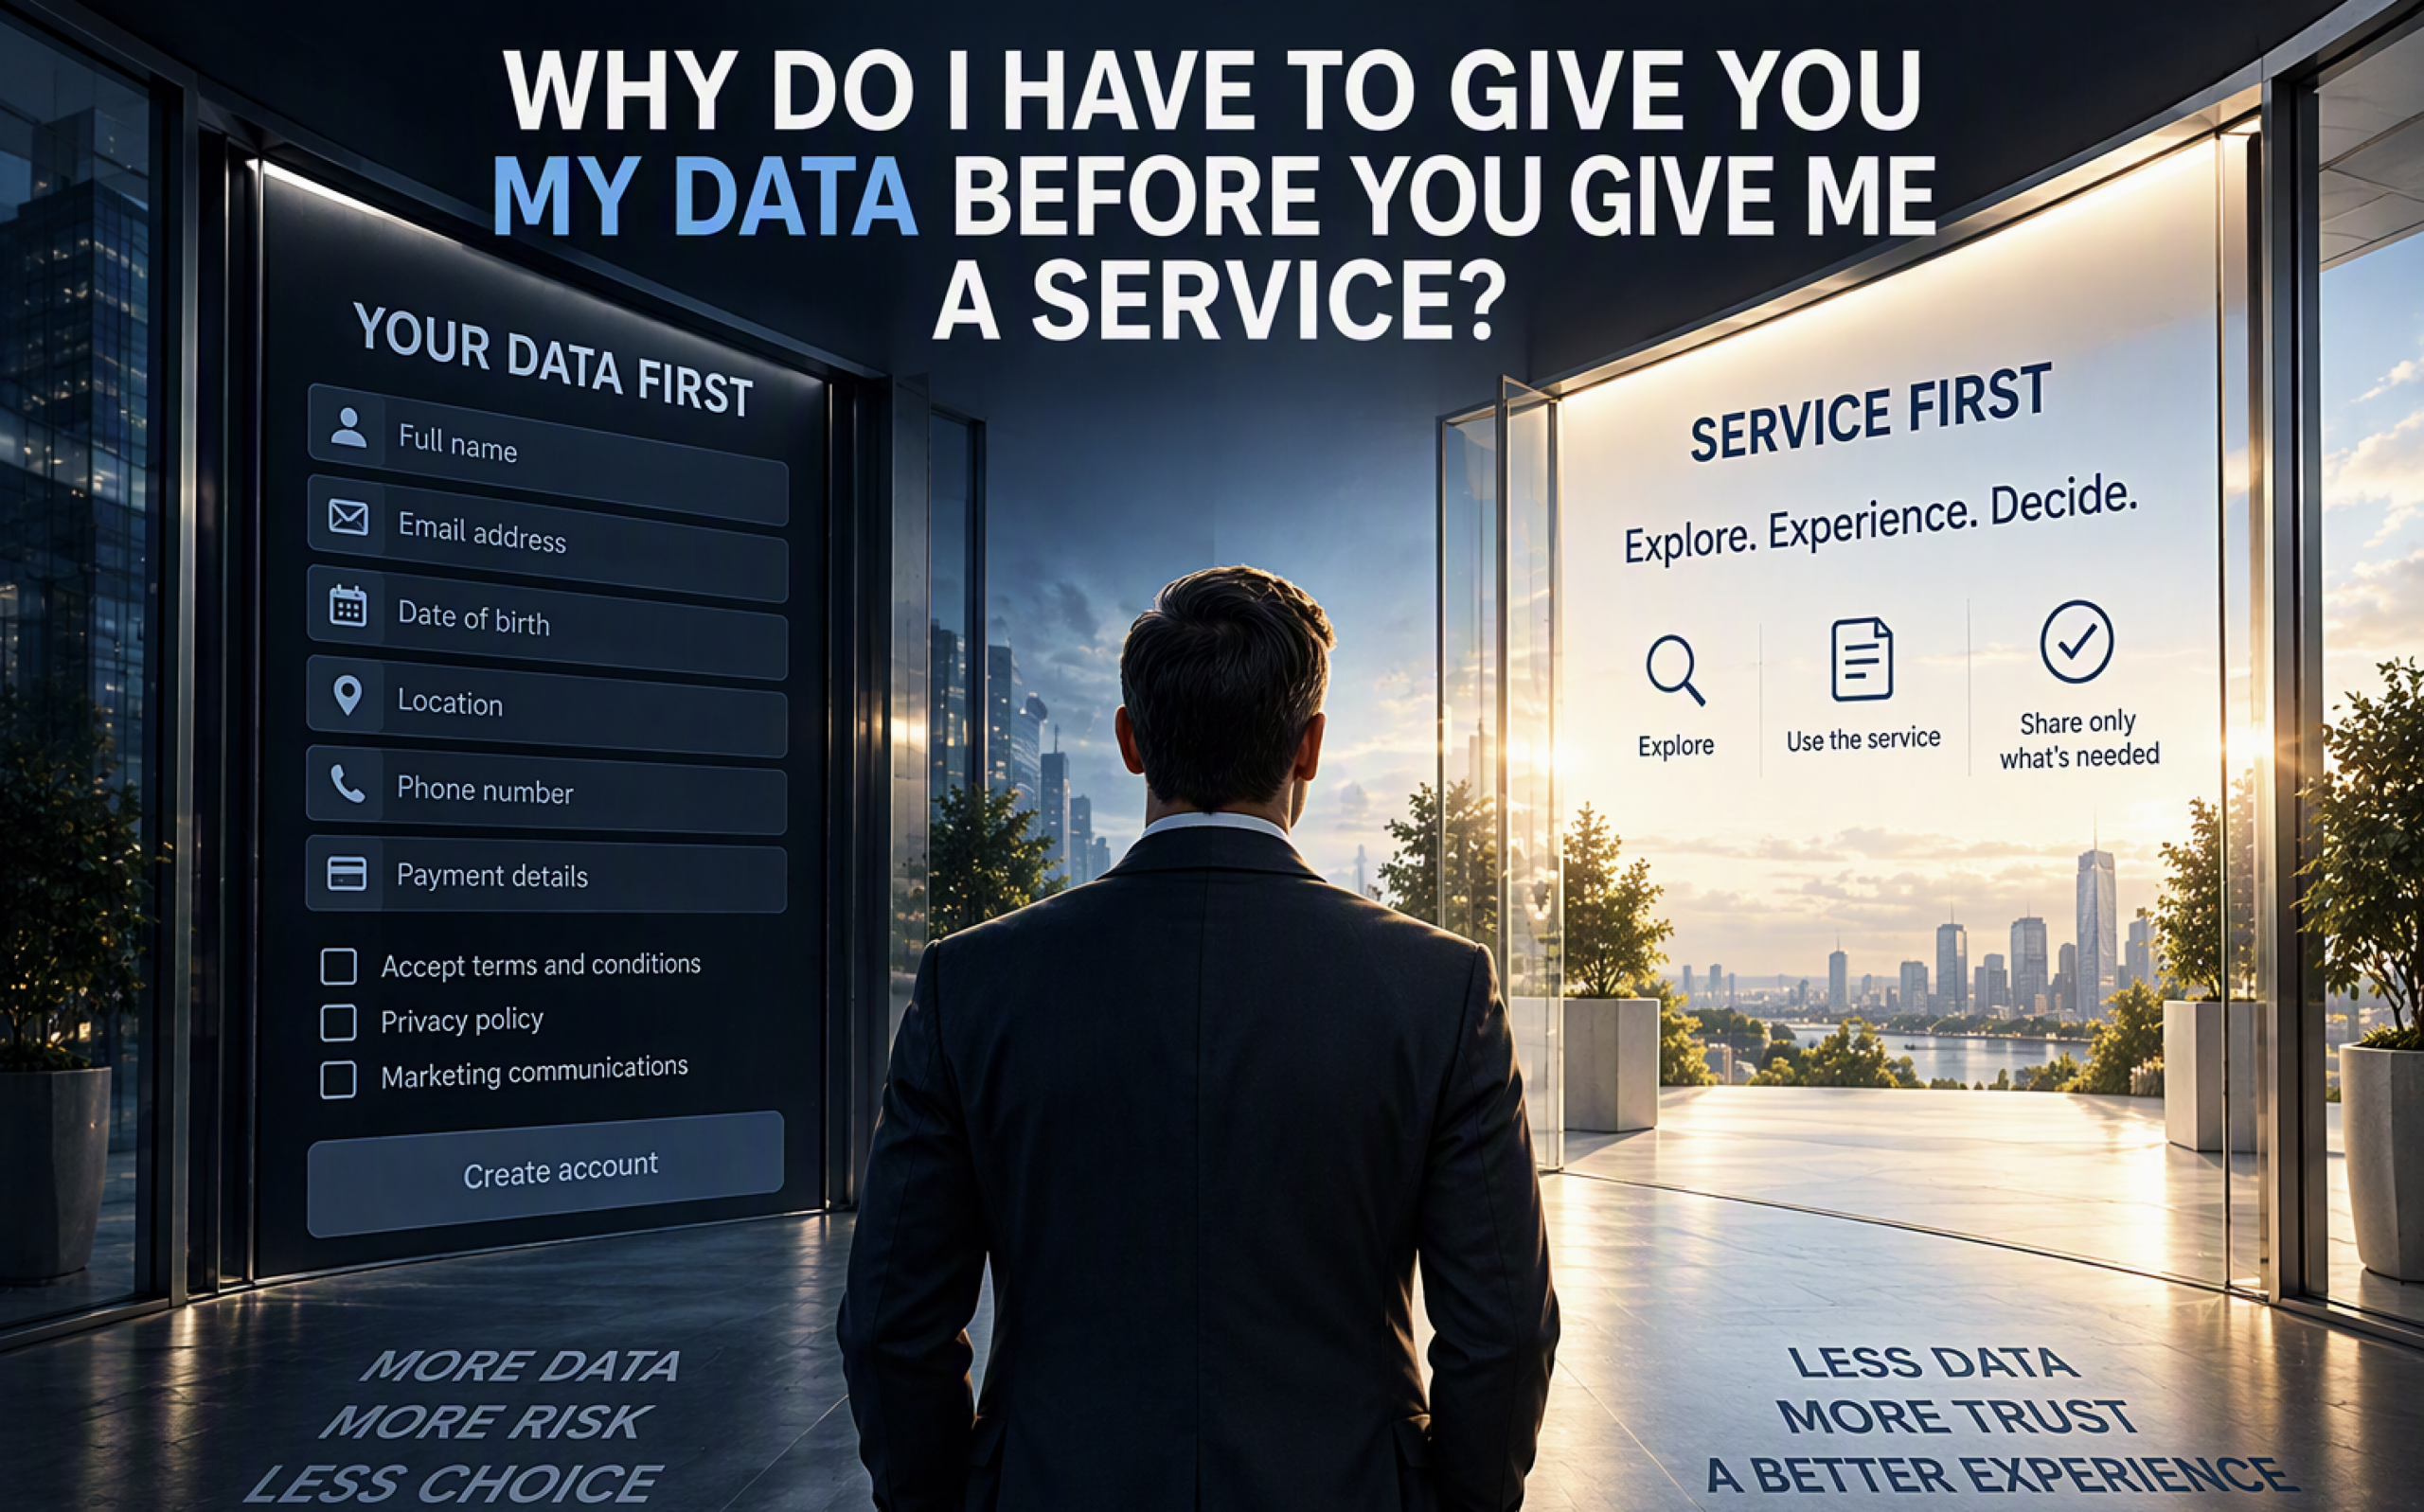
Every organisation makes promises.
- We will protect your data.
- We will respect your privacy.
- We will only use your information for the purposes described.
- We will not share it without permission.
- We invest heavily in policies, governance, compliance and security to make those promises credible.
And then we ask people to trust us.
But there is another question worth asking:
Why should they have to?
Trust has become part of the transaction
When I use a digital service, I am not simply buying something, communicating or completing a task.
I am often entering into an additional relationship.
I provide information.
The organisation promises to behave responsibly with it.
That promise might be backed by regulation, contracts, governance, security controls and considerable organisational effort.
But it remains a promise.
If the organisation can see the information, access the information or retain the information, someone ultimately has to be trusted to use it appropriately.
Perhaps there is another way to think about that relationship.
What if the promise became unnecessary?
Imagine an organisation saying:
You don’t have to trust us not to look because we cannot look.
That is fundamentally different from:
Trust us. We promise not to look.
The first depends upon the structure of the system.
The second depends upon the behaviour of the organisation and the people operating it.
This distinction sits behind ICCA Design Principles: Trustless by Architecture, Not Policy.
It does not argue that policies, governance or responsible leadership are unimportant.
It asks whether we should use them to control something that could, in some circumstances, be prevented structurally.
For a greenfield business
This creates an interesting opportunity.
When designing a new service, leaders can decide which promises the organisation should never need to make.
Instead of saying:
We collect this information, but we have controls governing its use.
Ask:
Could we design the service so that we never have access to it?
That potentially changes the conversation around trust from the beginning.
Trust is no longer created solely through reassurance.
Some of it is created through constraint.
For established organisations
Existing businesses cannot simply remove decades of technology, processes and information overnight.
Nor would that necessarily be desirable.
But leaders can begin somewhere much more practical.
Examine the promises you currently make to customers and ask:
Which of these promises exist because our systems allow us to do something customers don’t want us to do?
That is a very different way of looking at governance.
Each time we tell a customer:
“We won’t…”
there is an opportunity to ask:
Could we design the system so that we can’t?
From organisational trust to architectural trust
Good organisations should behave responsibly.
Good leaders should establish appropriate governance.
And good regulation remains important.
But architecture can create another layer of protection.
Policy says:
You are not allowed to do this.
Architecture can potentially say:
This cannot be done.
Those two ideas are not competitors.
But where the second is possible, relying exclusively on the first deserves questioning.
That is where the executive significance of this principle becomes particularly interesting.
An organisation may be able to reduce the number of things customers need to trust it not to do.
A question for leaders
Look at the promises your organisation makes about privacy, data and customer information.
Then ask:
How many of those promises could eventually become structural constraints rather than statements of intent?
Because perhaps the strongest form of digital trust is not:
Trust us to do the right thing.
Perhaps it is:
You don’t need to trust us. We designed it that way.
That is the adoption question behind ICCA Design Principles: Trustless by Architecture, Not Policy.
The underlying ICCA work is openly shared under a Creative Commons Attribution-ShareAlike 4.0 licence, encouraging discussion, challenge, adaptation and further development.
The paper describes the architectural principle. The article asks what adopting that principle could mean for leadership, organisations and the people who depend upon them.
#ICCA #DigitalTrust #TrustByDesign #PrivacyByDesign #Leadership #DataGovernance #DigitalTransformation #CustomerTrust #Governance #CreativeCommons